
Kubernetes & Container Platforms
A cluster (or a decision not to have one) with deploy, secrets, ingress, and capacity — so containers are a platform, not a weekend experiment.
Talk to an expert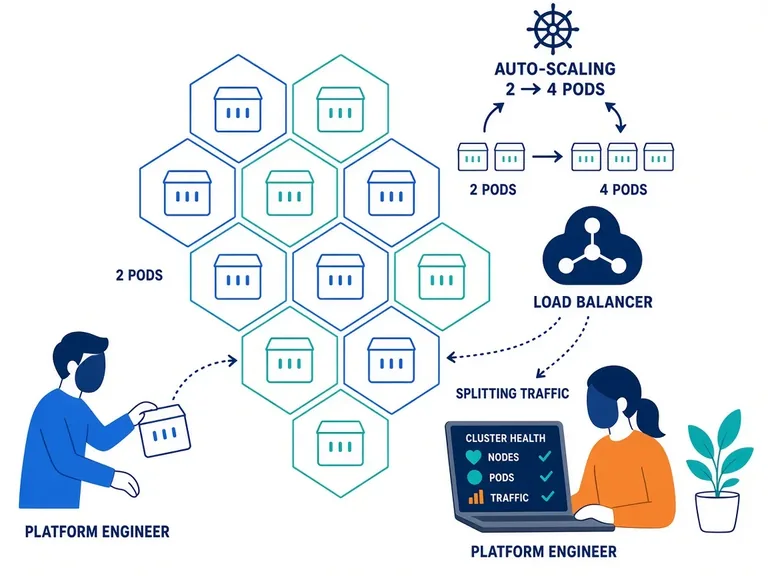
The offering
What we actually deliver
Containers without a platform become a second datacenter of YAML. We help you choose managed Kubernetes, a smaller container service, or no cluster at all when a PaaS would do. If a cluster is justified we build it in your account: node design, networking, ingress, secrets, storage, and the deploy path from CI. Add-ons are the ones you will patch, not a CNCF bingo card.
Workloads get resource requests, probes, and a namespace or tenancy model that matches your teams. We put observability and backup of cluster state on the same delivery. Upgrades are a planned activity with a test cluster; we do not leave you on a version the vendor will sunset during a freeze.
Local and CI builds produce the same images that run in production. Image provenance and a registry in your control are default. Cost is visible: idle nodes and replica sprawl are reviewed, because Kubernetes is good at hiding spend.
You get a platform a product team can deploy to with a documented path, and an operating model for upgrades and incidents. If Kubernetes is the wrong tool, we will say so and land you on the simpler one. Namespace or tenancy conventions, resource quotas, and who may create ClusterRoles are written down so the second team on the cluster does not recreate the access sprawl you just cleaned up.
What you get
How we work
A delivery path you can follow
Each engagement is sequenced so architecture, cutover, and handover are visible — not a black box at the end.
Talk to us about Kubernetes & Container Platforms
Share the current estate, deadline, and constraints — we will tell you what a first engagement should contain.